Security Engineering Without Hand-Waving: Core Architecture Deep Dives
Skipping vague security buzzwords—these technical notes unpack RFC 6238 TOTP cryptography, telecom vs offline threat models, and zero-knowledge E2EE design with animated diagrams and live Web Crypto labs.
How TOTP Works Under the Hood: Why Offline Authenticators Match Remote Servers Down to the Second
Even inside Airplane Mode with zero network traffic, an authenticator generates 6-digit codes matching GitHub, AWS, and Google simultaneously. Here is the deterministic math, HMAC security model, and real-world systems engineering behind RFC 6238.
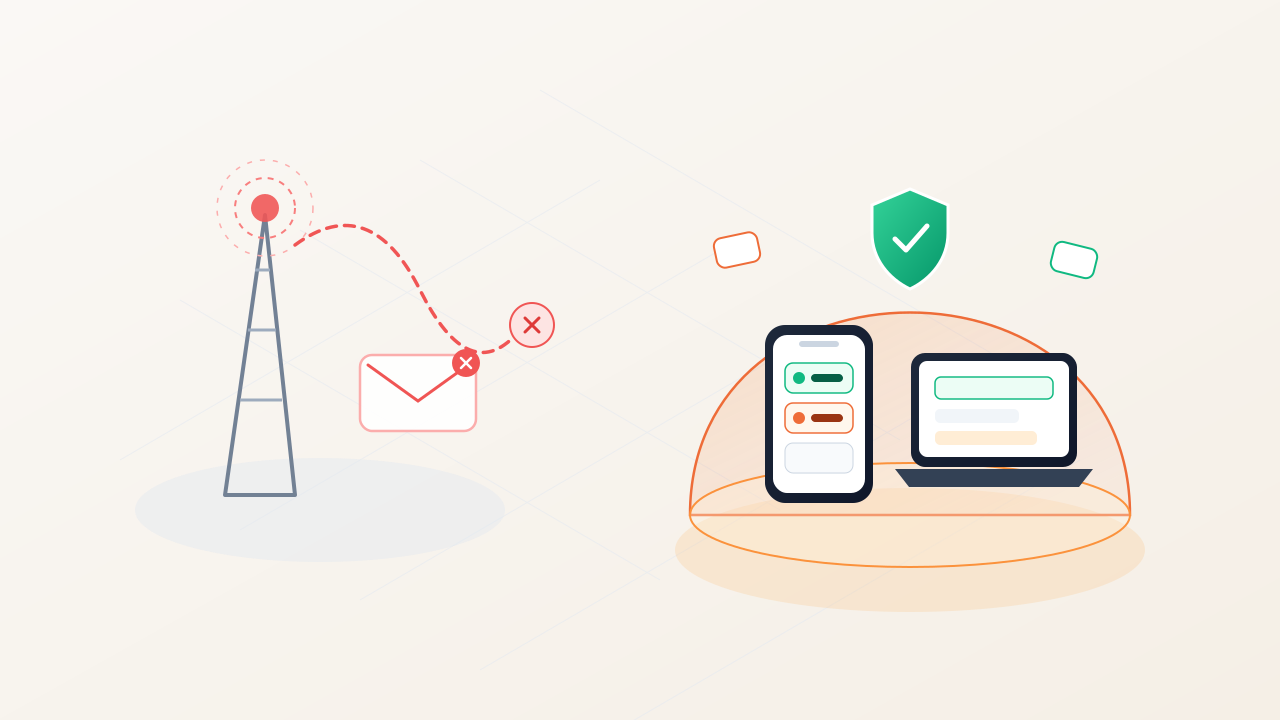
Why TOTP Outperforms SMS and Email Codes in Both Security and Real-World Reliability
Many people equate "Resend SMS" with reliability while fearing TOTP lockouts. When you examine network topology and attack surfaces side by side, external messaging relays turn out to be the weakest link—and modern E2EE vault architecture solves device loss without carrier trust.
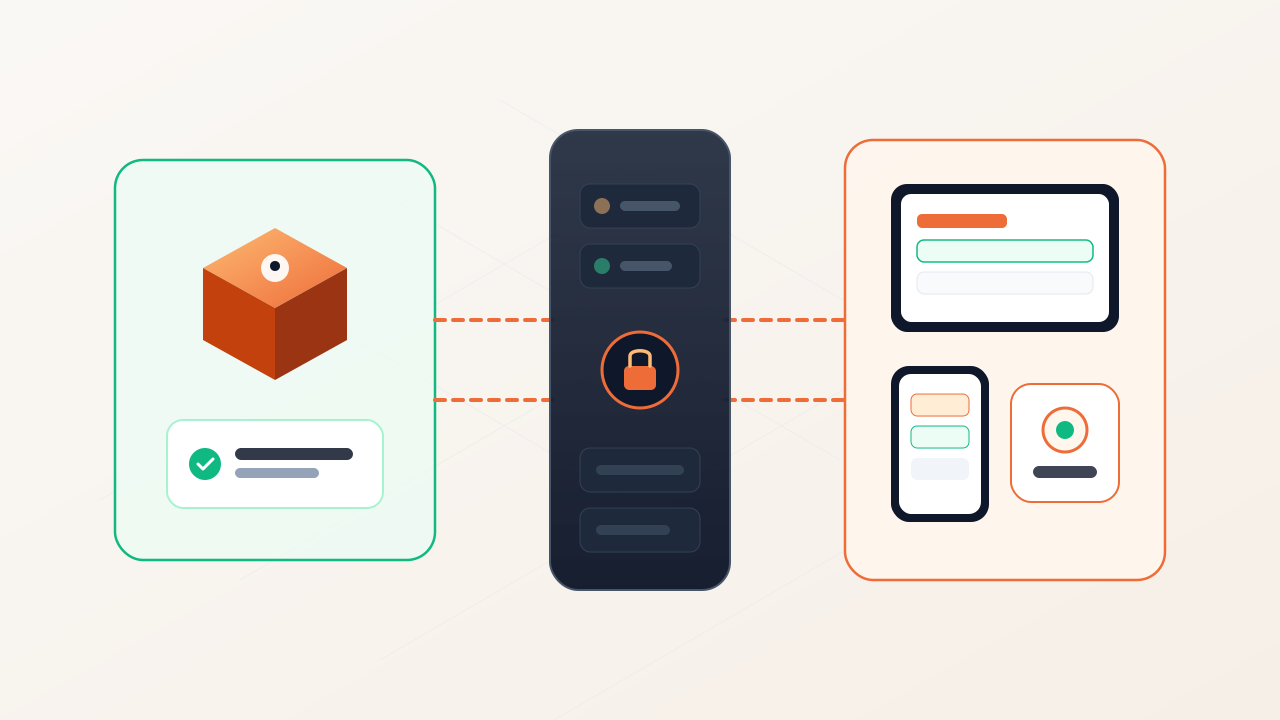
When the Cloud Is Just a Blind Wall: Designing a Zero-Knowledge E2EE Credential Vault
How can multiple devices stay automatically synchronized without duplicating tokens, while guaranteeing mathematically that a full server breach yields zero readable user secrets? Here are the core cryptographic boundaries and sync patterns.